System Settings Management
Introduction
The Settings sub-menu within iPassport QMS is the beating heart of system administration. Here many aspects of the system’s day-to-day operation can be managed. The Settings sub-menu is found within the Administration menu and is broken down into up to three tabs: Organisational Unit Preferences, Facility Preferences and System Preferences. Click the links to go to the articles about the first and the last of these.
The Facility Preferences tab is only available on enterprise accounts. On those accounts it appears for facility administrators, and for any user with the Manage Settings permission. It holds a single preference group, General Facility Preferences, which sets the Default Time Zone and the User Session Timeout for the facility. On a non-enterprise account the tab is not shown at all.
Navigate to Administration > Settings.
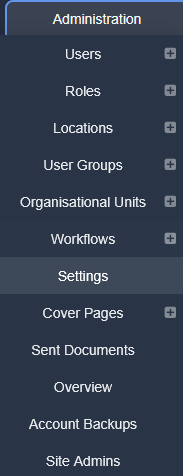
The system defaults to the System Preferences tab for users who hold the Manage Settings permission. The Administration > Settings menu item always opens System Preferences, so a user without that permission is taken somewhere else instead: to Facility Preferences if they are a facility administrator, or to Organisational Unit Preferences if they hold Organisational Units:Manage Settings. A user with none of these sees a message telling them they do not have access.

Global Settings & OU Specific Settings
Settings in iPassport are divided into two groups - global and OU specific. The (global) System Preferences settings affect the whole account. Any changes here will affect every record in all OUs and all users of the system. Changes to Organisational Unit Preferences settings only have an effect on the selected OU while all other OUs keep their existing settings.
On enterprise accounts there is a third, narrower scope: the settings on the Facility Preferences tab apply to the selected facility rather than to the whole account or to a single OU.
There is no overlap or contradiction between the global and system preferences; they do not have any direct effect on one another.
| Tip |
| Before changing any of the system preferences, it is always advisable to check with other administrators, as this change would affect the whole account. |
Copying preferences between OUs
Although editing an OU’s preferences only affects that OU, whole preference groups can be copied from one OU to others in a single, deliberate action.
On the Organisational Unit Preferences tab, select the OU whose settings are to be copied, tick the preference groups to copy in the list, then click Copy Preferences To. Select the destination OUs in the tree and click Copy Preferences.
Only OUs in which you hold Organisational Units:Manage Settings can be chosen as destinations, and the source OU itself is excluded. The copy is carried out as a background job, so allow a few minutes for the new settings to appear in the destination OUs.
| Warning |
| Copying preferences overwrites the existing preferences in every destination OU, and this action cannot be undone. Check the destination OUs carefully before confirming the copy. If Document Review Settings is one of the groups being copied, any documents in the destination OUs with an in-progress workflow may have those workflows restarted, and any workflow that is not available in the destination OU will not be set. |
| Note |
| The Menu/Tabs Translations group cannot be copied unless you are signed in as the admin user or as a site administrator. For everyone else it is left out of the list of groups to copy. |
Permissions
To access the global System Preferences, one major permission is required - Manage Settings. It’s only included in the system role, Administration Editor. Having this role in any given OU grants access to System Preferences. A separate permission, Organisational Units:Manage Settings (also included in the Administration Editor role), is what grants access to Organisational Unit Preferences, and it is needed within each given OU to manage that OU’s settings. Manage Settings is not required for the Organisational Unit Preferences tab. In other words, a user requires the role, Administration Editor in each OU where they need to access Organisational Unit Preferences.
A third permission, Desktop:Show Settings Menu Item (again included in Administration Editor), is what makes the Administration > Settings menu item appear. Because all three permissions sit in the same system role, this only matters when custom roles are being built: a custom role that grants Manage Settings without Desktop:Show Settings Menu Item gives a user access to Settings but no menu item to reach it with.
| Note |
| Some users reach Settings without being given these permissions at all: • the admin user, which is granted every permission in the system; • site administrators, who are likewise granted every permission; • facility administrators, who are granted every permission in the system for the facilities they administer. Conversely, a read-only user is restricted to the permissions held by the Global Viewer (excluding admin and personnel records) role, which does not include Manage Settings. A read-only user therefore cannot reach Settings even if they have been given the Administration Editor role, and that restriction is applied ahead of the site administrator exception, so a read-only site administrator is blocked as well. |
| Info |
Settings control many aspects of iPassport QMS. As a general rule, they do not need to be looked at prior to any information being added to a new account. However, they should be part of the implementation phase of any project as they can help set up the system to suit requirements. For example, the System Preferences area has options for ‘User Logon Settings’ that include ‘Minimum Password Length’ and ‘Password Expires after (days)’. These can be important settings to consider before allowing users to log in. |
| Note |
| The User Logon Settings group is not a free choice: minimum values are enforced when the group is saved. Minimum Password Length must be at least 8, and Lockout period must be at least 1 minute. A lower value is rejected with a warning and the group is not saved. These minimums are not applied when the account’s login strategy is already saved as SAML. Note that it is the saved value that is checked, not a change to the login strategy being submitted at the same time. |
Next step:
The next article covers Organisational Unit Preferences
Was this article helpful?
That’s Great!
Thank you for your feedback
Sorry! We couldn't be helpful
Thank you for your feedback
Feedback sent
We appreciate your effort and will try to fix the article